
Functional interfaces, discovery, power limits and serviceability
Abstract
A modular sensor node can reuse a common communication and computation core across location, acoustic and environmental sensing tasks. Such extensibility is valuable only when mechanical interfaces, electrical limits, software identification and security are defined consistently. This paper analyzes the modular node concept of MESH2026 and develops a system architecture separating a mesh base, functional expansion modules and a protected supply subsystem. It proposes constraints for safe recognition, feature discovery, energy budgeting and in field replacement. The discussion includes integration risks specific to antenna placement, microphone access and outdoor service. The output is a design framework and verification matrix, not a report of a manufactured prototype test.
Keywords: wireless mesh networks; sensor networks; modular mesh sensor nodes; analytical modeling; reliability; network design.
1 Introduction
Wireless mesh designs connect nodes using multiple wireless links and forwarding relays, but the existence of an alternate link does not by itself guarantee end to end service. Performance depends on radio quality, control traffic, source reporting rates, topology changes and gateway capacity. This study addresses one distinct subset of those coupled design concerns, using the models and engineering constraints developed in MESH2026-v07. Its findings are analytical statements with explicit assumptions rather than claims about a completed controlled deployment.
The objective is to define a technically traceable decision framework that converts the supplied study into testable engineering criteria. The manuscript draws solely on the source report and bibliographic entries present in that report. References retain the original source numbering so each item can be reconciled directly with the underlying bibliography. No new externally obtained sources are introduced.
2 Analytical Scope and Method
The method proceeds by identifying the system boundary, selecting a small number of measurable state variables, deriving a simplified relationship or comparison, and then distinguishing mathematical consequences from assumptions that require experimental verification. Conceptual drawings show component or information relationships; calculated charts visualize nominal conditions. They are not field measurements. This separation is especially important in wireless systems, where terrain, interference, retransmission policy and time synchronization can dominate apparent theoretical advantage.
Source basis: MESH2026-v07, sections 3.7, 3.8. Reference numbers preserve the numbering of its chapter 7 bibliography. The analytical figures are original illustrations of stated assumptions, not experimental observations.
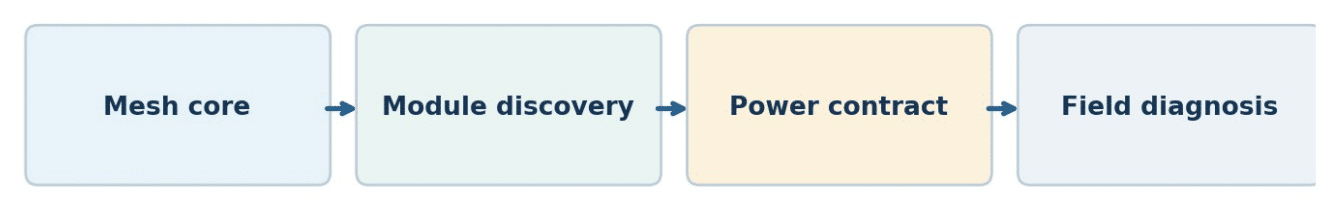
Figure 1. Functional architecture developed from the relevant MESH2026 concepts; schematic, not a tested implementation.
3 A reusable mesh core
The central communication module combines a controller, radio interface, local identity and firmware capable of joining and maintaining network links. It acts as a host for application modules rather than requiring every sensor to become a distinct mesh network participant. The separation creates a stable communication platform that can be reused across multiple field missions. The core must still expose enough diagnostic state to identify a faulty module without masking the reason for a loss of communication.
Examples described in MESH2026 include position modules, acoustic sensing, additional environmental sensors, nonvolatile storage and interchangeable power arrangements. A GPS module may have specific antenna and timing requirements; a microphone requires an unobstructed acoustic path and controlled sampling current. A supply module must advertise its available energy and protect against insertion, reverse current and radio transmit transients. Modular design thus combines software interchangeability with concrete physical restrictions. [76], [102].
Figure 2. Calculated or qualitative illustration of the design mechanism. Axes and assumptions are described in the main text.
4 Interface and module compatibility
A field interface has at least four contracts: connector geometry and locking, supply voltage and maximum current, communication protocol and pin assignment, and the software identity of the attached module. Each contract should be versioned. A compatible physical connector alone does not mean that two boards are electrically or logically compatible. A module that draws excess startup current can reset the entire mesh node and disrupt relaying for downstream devices.
During insertion, the host should discover module identity and declared capabilities, check its supported revision, measure or bound the power load, and then enable only permitted functions. If the module is unknown or violates limits, the host should fail into a defined safe state and report the cause. Automatic detection may use a machine readable descriptor, but the descriptor itself must be protected against unauthorized substitution for security-sensitive modules. [91], [98].
Table 1. Scope of the principal design comparison.
Module Primary function Integration acceptance condition
Mesh base Identity, routing and control Stable join and diagnostic state
Location GNSS position and time Antenna placement / timing
Acoustic Sound event acquisition Unobstructed port / duty limits
Power Supply and charge reporting Peak pulse and cutoff margins
Storage Local event buffering Data integrity after power loss
5 Power budgeting changes when modules change
A sensor package may alternate between sleep, periodic measurements, event triggered acquisition and continuous routing. Its power envelope changes whenever a module is attached or removed. A node should revise its lifetime forecast from charge per event, sensor duty and relay forwarding rate after a configuration change. Such recalculation is necessary because a module’s low standby current does not imply low operating energy.
Peak demands must also be considered. A radio transmit burst can coincide with a GPS acquisition or memory write. Battery impedance and cold temperatures may then cause voltage collapse even though the estimated average current appears acceptable. Supply architecture and firmware scheduling should reduce simultaneous peak loads and record the conditions under which module operation is throttled. [88], [103].
6 Field mechanics and environmental exposure
A quick connection mechanism may use a rail, keyed plug or secured short cable. The choice depends on gloves, mounting orientation, antenna clearance, ingress protection and service speed. Uncontrolled stacking can shield GNSS antennas or block an acoustic port. Repeated replacements wear seals and connectors, so service life must be qualified as part of the enclosure design.
The source technical study separately discusses dust and water ingress, vibration, shock, temperature, sunlight and corrosion. A modular node requires these tests for the assembled configuration, including its antenna and cables. A component certificate does not automatically cover a new combination of modules and housing. Maintenance procedures should define permitted substitutions and the post-replacement checks necessary before return to service. [99], [100], [104].
Evaluation parameters
A reproducible trial should log per-node packet identifiers, generation and reception timestamps, route changes, radio retransmissions, queue age and battery current. All measurement and reporting intervals, payload formats, antenna geometry and firmware revisions should be recorded. Reliability must be reported with variation over trials, not as a single best-run percentage. A successful link in one season or installation position is not equivalent to a verified network-level service guarantee.
7 Validation and applicability
A verification campaign should test compatible and incompatible attachments, insertion under low voltage, repeated mating cycles, brownout recovery, module discovery latency, updated energy estimates and correct routing continuity during service. Physical tests must include the exact packaging and mounting profile intended for use. Diagnostic logs should record firmware revision, module revision and the reason for accepting or rejecting a configuration.
This work does not determine the final connector or module bus. Those choices require detailed electrical, electromagnetic and mechanical qualification. Its contribution is a modular architecture and validation contract that prevents field convenience from undermining network trust or availability. [95], [96].
8 Reproducible Experiment Design
Modular integration verification
Test the mesh core with every permitted module alone and with the highest allowed combined load. Insert unsupported and deliberately incompatible test modules only on a protected bench. Record discovery result, error handling and voltage stability under simultaneous radio and sensor peaks. Repeat after the stated connector endurance cycles and in assembled environmental packaging.
All trials should state the hypothesis before measurements begin. In particular, baseline and modified networks must generate a comparable number of application messages under identical payload semantics. Time synchronization, radio configuration, antenna placement and test duration should be documented. Apply a predefined definition of a valid delivery, including how duplicate frames, acknowledgements, partial packets and expired records are treated. Report distributions and uncertainty rather than interpreting isolated examples as population-level network behavior.
The primary measurement vector is: Module identity, start-up voltage, current margin, discovery time, interface errors and routing continuity. The experiment should archive raw records and configuration files so that independent reviewers can reconstruct packet success, route depth and energy exposure. Failed configurations and unavailable nodes must remain in the results table rather than being discarded as outliers. Where an event is delayed by buffering, store both the origin timestamp and the gateway arrival timestamp to avoid falsely classifying a stale packet as timely delivery.
9 Model Sensitivity and Acceptance Criteria
A design parameter has operational meaning only relative to an application threshold. For packet delivery, an acceptable loss ratio may differ between a periodic weather reading and an emergency alarm. For latency, a median value can be misleading when occasional extreme delay is harmful. Therefore the acceptance plan should name the threshold and its aggregation level: individual node, gateway sector or whole deployment. At minimum, retain a reliability target, a maximum age for useful data, and a minimum expected autonomy for each energy role.
Sensitivity analysis should vary one major assumption at a time and then test coupled effects. Candidate variables include per-hop reception probability, reporting frequency, number of downstream children, active listening duration, gateway count and available battery capacity. An improvement observed under one parameter combination may disappear when the network is congested or when temperature reduces battery availability. The purpose of a sensitivity plot is to identify which physical measurement would most change the final design decision, not to predict field performance without evidence.
A mechanically fitting connector is not proof of bus compatibility, safety or environmental rating for the full assembled product.
A final acceptance matrix should include four outcomes: the test condition, the expected service limit, the observed numerical result and the engineering decision. The source technical study supports the selection of variables and design mechanisms, but a numerical pass/fail result requires an actual implemented protocol and controlled measurements. The distinction prevents a model assumption from being silently promoted to verified specification.
Evaluation scenario matrix
Scenario Variable held constant Question to resolve
Same radio / payload / gateway Does the reference service meet its Nominal baseline position target?
Same node count and physical Does age or packet loss rise before a Increased offered traffic layout stated limit?
Can useful records still reach the Relay or link interruption Same sensor sample generation gateway?
Same routing and application Which role becomes the limiting Reduced energy reserve service component?
Does adaptation improve the Configuration change Same declared application goal system-level outcome?
The nominal baseline provides a necessary denominator for every claimed improvement. A second, more demanding workload should keep the number and location of devices unchanged, which helps isolate the effect of the altered report rate or route policy. The failure trial should define in advance whether losing the first packet after an outage counts as unacceptable service or whether a bounded recovery period is allowed. A device can legitimately buffer packets for later transfer, but the resulting data age must be visible in the assessment.
Energy experiments should compare the same battery assumptions and device roles. A measured reduction in the charge consumed by a leaf node may be offset by increased listening or forwarding costs in its parent. The appropriate system measure is therefore not simply the largest lifetime estimate in the network; it is the minimum acceptable service continuity across critical coverage points. Temperature, battery cutoff and intermittent backhaul availability may change which node becomes critical even when network geometry is unchanged.
Finally, sensitivity should be reported as an envelope rather than an unexplained single-number promise. State which parameters were deliberately changed, identify the origin of every numerical assumption, and preserve the complete measured distribution if physical tests are later performed. When the source provides only theoretical values, label the result a calculation or hypothesis. This audit trail makes the framework useful for deciding the next experiment and reduces the risk that an optimistic reference scenario will be mistaken for a certified operating limit.
10 Discussion
The analysis points to a recurring challenge: radio reach, packet reliability, bounded latency and energy endurance are not independently optimizable in a shared forwarding network. Improving one dimension can worsen another. Greater redundancy adds possible routes but can increase scanning or contention. More frequent reporting improves data freshness but increases relay burden. Stronger integrity protection changes frame overhead and configuration responsibilities. These effects require a scenario specific performance contract before hardware or protocol claims can be generalized.
The most defensible next step is a measured comparison with a declared baseline and pre- registered acceptance thresholds. Test design should preserve the conditions under which the mathematical assumptions are approximately valid, document deviations, and present limits as prominently as advantages. This article supplies an analytical framework suitable for subsequent empirical investigation but does not claim experimental superiority or compliance certification.
11 Conclusion
The MESH2026 material supports a structured analytical treatment of modular architecture of configurable mesh sensor nodes for field deployment. The resulting framework separates topology, traffic, radio and energy constraints, supplies scenario dependent decision criteria, and defines a path to experimental verification. The final engineering choice should be guided by the application’s maximum data age, required delivery probability, actual relay workload and maintainability under failure. Numerical examples are conditional calculations, and validation against physical deployments remains necessary.
References
[76] Texas Instruments, CC2652R data sheet and product documentation, listed in MESH2026 bibliography.
[88] Texas Instruments, BQ25570 data sheet and product documentation, listed in MESH2026 bibliography.
[91] M. Vučinić et al., Constrained Join Protocol for 6TiSCH, RFC 9031, 2021. DOI 10.17487/RFC9031.
[95] B. Moran et al., A Firmware Update Architecture for Internet of Things, RFC 9019, 2021. DOI 10.17487/RFC9019.
[96] B. Moran et al., A Manifest Information Model for Firmware Updates in IoT, RFC 9124, 2022. DOI 10.17487/RFC9124.
[98] M. Fagan et al., IoT Device Cybersecurity Capability Core Baseline, NISTIR 8259A, 2020. DOI 10.6028/NIST.IR.8259A.
[99] USB Implementers Forum, USB Type-C Locking Connector Specification, 2024.
[100] IEC 60529, Degrees of protection provided by enclosures (IP Code), ed. 2.2, 2013.
[102] MIKROE, Introducing ClickID, 2023.
[103] Texas Instruments, LM5069 data sheet and product documentation, listed in MESH2026 bibliography.
[104] IEC 60512-9-1, Connectors for electronic equipment—Mechanical operation test, 2010.
[M] MESH2026-v07. Technical study, sections 3.7, 3.8. Unpublished technical material.
Pridaj komentár